GitLab Vulnerabilities, November 2026: Update to 19.6.1
Contents10
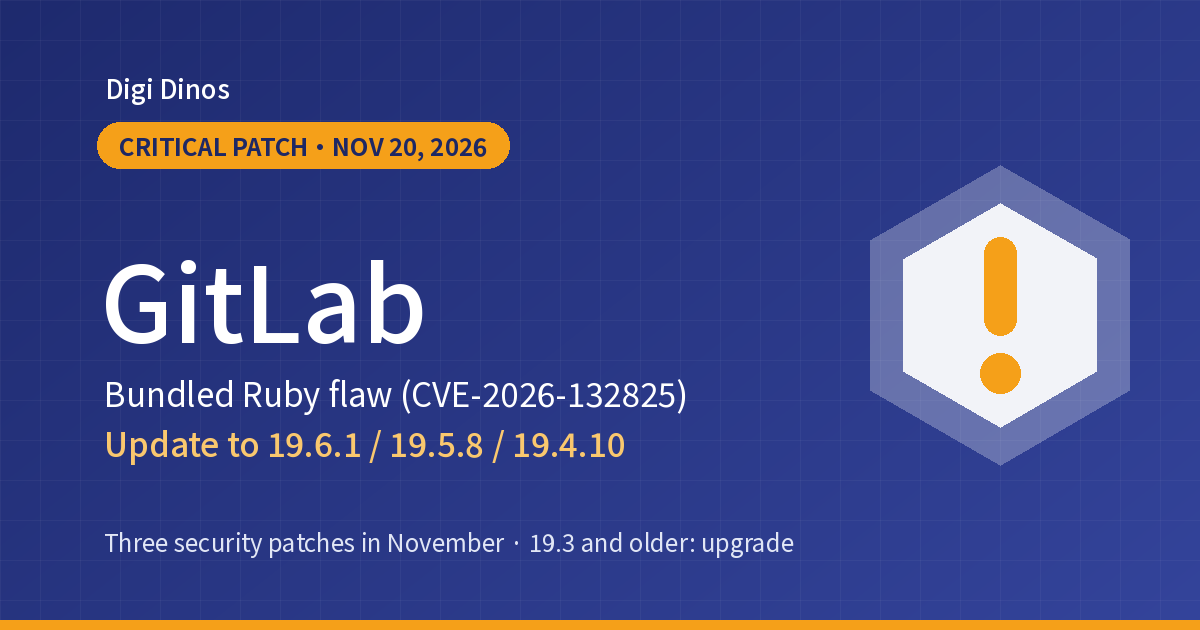
On 20 November 2026 GitLab released urgent fixes, GitLab 19.6.1, 19.5.8 and 19.4.10. The reason: a vulnerability (CVE-2026-132825) in Ruby, the programming language GitLab runs on, that may let an attacker run code from outside using a specially crafted string. This is the third security fix in November, after a Critical fix on the 10th and 37 fixes on the 16th.
This article is for companies that run GitLab on their own servers and for those whose source code sits on their development vendor's GitLab: what November's fixes contain, which version to move to, and what to check. For the October vulnerability (CVE-2026-97229), see "What to Do About the GitLab Vulnerability".
Key takeaways
- You run GitLab on your own server → Update to 19.6.1, 19.5.8 or 19.4.10 or later.
- GitLab.com and GitLab Dedicated (the dedicated cloud edition) have already been patched by GitLab. Users do not need to do anything.
- The 20 November fix covers only three branches: 19.6, 19.5 and 19.4. If you are on 19.3 or older, you need to update to 19.4.10 or later.
- If you did not install GitLab from the official packages, you must also reinstall Ruby at 3.3.14 or 3.4.13 or later.
3
Security fixes in November (10th, 16th and 20th)
2
Of those, Critical vulnerabilities (git and Ruby)
37
Vulnerabilities fixed in the regular 16 November release
Terms used here
GitLab = a system that stores source code, lets a team work on it together, and tests and deploys it automatically. You can install it on your own server (self-managed) or use the cloud service, GitLab.com.
Ruby = the programming language GitLab is built with. It is also used by web services built with Ruby on Rails.
Gitaly = the part of GitLab that handles repositories (where the source code is stored).
KEV = the list of "vulnerabilities known to be exploited in real attacks" published by the US agency CISA.
November's three fixes
- Urgent fix (19.5.4 / 19.4.6 / 19.3.8). Fixes CVE-2026-105437 (Critical) in the git bundled with GitLab. Under certain conditions, an attacker could run any command they like in the Gitaly environment.
- Regular fix (19.5.6 / 19.4.8 / 19.3.9). Fixes 37 vulnerabilities (4 High, 24 Medium, 9 Low).
- Ruby releases fixes: Ruby 4.0.10, 3.4.13 and 3.3.14, fixing 7 vulnerabilities in regular-expression and string handling.
- GitLab 19.6 released (the monthly new version).
- Urgent fix (19.6.1 / 19.5.8 / 19.4.10). Fixes the Ruby vulnerability CVE-2026-132825 and others by updating the bundled Ruby.
The 20 November fix: the Ruby vulnerability
According to GitLab, CVE-2026-132825 is a bug in which Ruby writes outside its memory bounds when converting a string between upper and lower case. If a crafted string is converted, memory can be corrupted under certain conditions. The Ruby team says that in some cases it may let an attacker run code from outside (remote code execution).
The Ruby team rates it Critical; MITRE (the organisation that manages CVE numbers) rates it High (CVSS 7.4). GitLab follows Ruby's rating and calls it Critical. The 20 November releases also include the other 6 fixes Ruby announced on 18 November.
| Branch | Hit by CVE-2026-132825 | Move to |
|---|---|---|
| 19.6 | 19.6.0 | 19.6.1 or later |
| 19.5 | 19.5.7 and earlier | 19.5.8 or later |
| 19.4 | 19.4.9 and earlier | 19.4.10 or later |
| 19.3 and older | All versions | No fix for this branch. Move to 19.4.10 or later |
※ GitLab lists every version before 19.4.10 as affected. The latest 19.3 release is 19.3.9 from 16 November, but it does not include the Ruby fix.
※ GitLab Dedicated got the fix earlier, in internal versions (19.5.7 and 19.4.9). Because 19.5.7 and 19.4.9 were not released publicly, self-managed users should use 19.5.8 and 19.4.10.
Updating GitLab may not be enough
This fix replaces the Ruby bundled with GitLab. GitLab's official Linux packages and container images already include the fixed Ruby. But if you built GitLab from source yourself, you need to reinstall the Ruby that runs GitLab at 3.3.14 or 3.4.13 or later (a newer release of the same branch is also fine). The October vulnerability came with the same warning.
The 10 and 16 November fixes
The urgent fix on 10 November addressed a vulnerability in the git bundled with GitLab (CVE-2026-105437, Critical). According to GitLab, under certain conditions memory could be written out of bounds, and an attacker could run any command they like in the Gitaly environment. Affected are versions from GitLab 16.2 onwards before 19.3.8, 19.4.6 and 19.5.4. GitLab has also published detection rules to spot exploitation attempts.
The regular fix on 16 November addressed 37 vulnerabilities. All 4 rated High involve exploitation by a logged-in user.
| Vulnerability | What it does | Severity (CVSS) |
|---|---|---|
| CVE-2026-105739 | A wiki page may run malicious code (JavaScript) in the browser of anyone who views it | 8.7 |
| CVE-2026-108153 | The Error Tracking screen may likewise run malicious JavaScript | 8.7 |
| CVE-2026-18241 | A gap in the permission check for CI/CD jobs (a race condition) may let protected CI/CD variables (such as production keys) be read | 8.2 |
| CVE-2026-97187 | The workspaces feature may let secret information (Secrets) stored elsewhere in a Kubernetes cluster connected to GitLab be read | 7.6 |
※ Updating to 19.6.1, 19.5.8 or 19.4.10 also brings in the 10 and 16 November fixes.
Exploitation status (as of 21 November 2026)
The vulnerabilities fixed in November (CVE-2026-132825, CVE-2026-105437 and the 4 High issues from 16 November) are not on CISA's KEV list (20 November edition). We also could not find any statement in GitLab's announcements that exploitation has been confirmed. In the lists of security alerts from IPA and JPCERT/CC (checked 21 November), we could not find any alert covering these GitLab or Ruby vulnerabilities either.
However, the Ruby team says it is aware that proof-of-concept code (PoC) leading to remote code execution exists for some of the vulnerabilities. And the October GitLab vulnerability (CVE-2026-97229) was added to KEV about two and a half weeks after the fix was released. We recommend updating soon.
Five steps to check and respond
- Find out where your GitLab runs
On your own server, in the cloud (AWS and so on), or GitLab.com? If a vendor looks after your code, it may live on their GitLab.
- Check the version and how it was installed
Sign in to GitLab and check the version under "Help". Also check whether it was installed from the official package (Omnibus) or official container, or built from source.
- Update to the latest release of your branch
Go at least to the "Move to" column above. On 19.3 or older, move to 19.4.10 or later. For a big version jump, you need to step through the intermediate versions GitLab specifies (the upgrade path) in order.
- If you built from source, update Ruby too
Reinstall the Ruby that runs GitLab at 3.3.14 or 3.4.13 or later.
- Look for suspicious activity
Look for accounts you don't recognise, changes to administrator permissions, newly created CI/CD variables or access tokens, and Gitaly processes crashing. If anything looks suspicious, regenerate your tokens and keys.
If your vendor holds your source code
If your source code or production keys sit on your vendor's GitLab, try asking them:
- "Has your GitLab been updated to the 20 November fixes (19.6.1, 19.5.8, 19.4.10)?"
- "If your GitLab is built from source, have you updated Ruby too?"
- "Who can see the production passwords and keys stored in CI/CD?"
Check your other Ruby systems too
This Ruby vulnerability is not just a GitLab problem. For your own web services built with Ruby, such as Ruby on Rails apps, update Ruby to 4.0.10, 3.4.13 or 3.3.14 or later as well. According to the Ruby team, Ruby 3.2 and older are no longer supported and will not get this fix. Some of the regular-expression vulnerabilities are especially dangerous in apps that use regular expressions entered by users as they are.
Leave it, or act now?
If you leave it
- Source code and production keys may be stolen
- Attackers may get into your production environment through CI/CD
- Older branches stay unpatched, with no fix coming
If you update and review
- All three of November's fixes are applied at once
- You can tidy up CI/CD variables and permissions
- You are ready to respond quickly to the next urgent fix
How Digi Dinos can help
Digi Dinos supports companies with DX, security, and system operation and maintenance. We are ISO 27001 certified, and we also handle the operation of development platforms such as GitLab and servers, plus 24/7 monitoring (NOC). Our team works in Japanese.
- GitLab updates: we take a backup and check the upgrade path before updating.
- Permission and secrets review: we review CI/CD variables, access tokens and administrator accounts.
- Taking over operations: we can also take over the operation of GitLab and servers previously managed by another company.
Not sure your GitLab is safe? Free consultation.
From checking the version to planning the update, we guide you in Japanese.
Frequently asked questions
We only use GitLab.com. Do we need to do anything?
According to GitLab, GitLab.com and GitLab Dedicated have already been patched, and users do not need to do anything. However, any Runners you set up yourself (the servers that run CI/CD jobs) are your responsibility. Keep the OS and software on your Runner servers up to date too.
We updated to 19.5.6 on 16 November. Is that enough?
No. 19.5.6 does not include the Ruby fix (CVE-2026-132825). Please update to 19.5.8 or later.
We are on 19.3. Is 19.3.9 OK?
19.3.9 does not include the Ruby fix. The 20 November fixes cover only three branches, 19.6, 19.5 and 19.4, so please update to 19.4.10 or later.
Sources (checked 21 November 2026)
- GitLab, "GitLab Critical Patch Release: 19.6.1, 19.5.8, 19.4.10" (20 November 2026)
- GitLab, "GitLab Patch Release: 19.5.6, 19.4.8, 19.3.9" (16 November 2026)
- GitLab, "GitLab Critical Patch Release: 19.5.4, 19.4.6, 19.3.8" (10 November 2026)
- Ruby, "Security advisories: multiple vulnerabilities in Regexp and String case conversion" (18 November 2026)
- CISA, "Known Exploited Vulnerabilities Catalog" (20 November 2026 edition)
Related articles
PHP Vulnerabilities, November 2026: 7 Critical Flaws and Fixes
Java4Shell (CVE-2026-114938): Who Is Affected and How to Fix It
NGINX Vulnerabilities: HTTP/2 RCE and Version 1.30.7
Check Point CVE-2026-123039: Exploited with PHP2Shell
Microsoft 365 Outage, November 2026: Cause and Recovery
Microsoft November 2026 Updates: Exploited Outlook Flaw and KBs
OpenSSH CVE-2026-123158: Alpine Login Bypass and What to Do
Japan Data Breaches, Early November 2026: A Summary
Arara Message Breach Update: About 81 Million Email Addresses
SonicWall SSLVPN CVE-2026-19868: MFA Bypass and What to Do
Apache Tomcat Vulnerabilities, October 2026: 8 Flaws and Fixes
.NET 8 and 9 End of Support on 10 November 2026: What to Do
Movable Type Vulnerability JVN#91153973: Update or Mitigate Now
WordPress CVE-2026-119977: Listed as Exploited, Update Now
Japan Data Breaches, Oct–Nov 2026: What Companies Should Check
Ivanti Connect Secure Zero-Days: Update Again and Investigate
GitLab CVE-2026-97229 (CVSS 10): Exploited, Patch Now
Linux Kernel Fragnesia (CVE-2026-46300): Exploited, Patch Now
Brotli Vulnerability CVE-2026-111497 (HTTP2Shell): What to Do
PHP Vulnerability CVE-2026-109618 (PHP2shell): What to Do Now
PHP Upgrade Cost: Moving From PHP 5 or 7 to PHP 8
Taking Over a Legacy System With No Documentation
Node.js Security Release, October 2026: What to Do
Java Vulnerabilities, November 2026: Versions to Install
Securing Legacy Systems: Where to Start (2026 EOL Guide)
Superior Features of ChatGPT 4o (4 Omni)
What Is Digital Transformation? Definition, Roadmap and Examples
The Secret to Happiness!
What Is an IT Comtor? Role, Skills and How It Differs from a BrSE